
Are Online Loan Request Forms Safe on Public Wi-Fi?
SSL encryption and smart habits can make online loan request forms safer on public Wi-Fi, but you need to verify the site and avoid shared networks when possible.
By David Wheeler
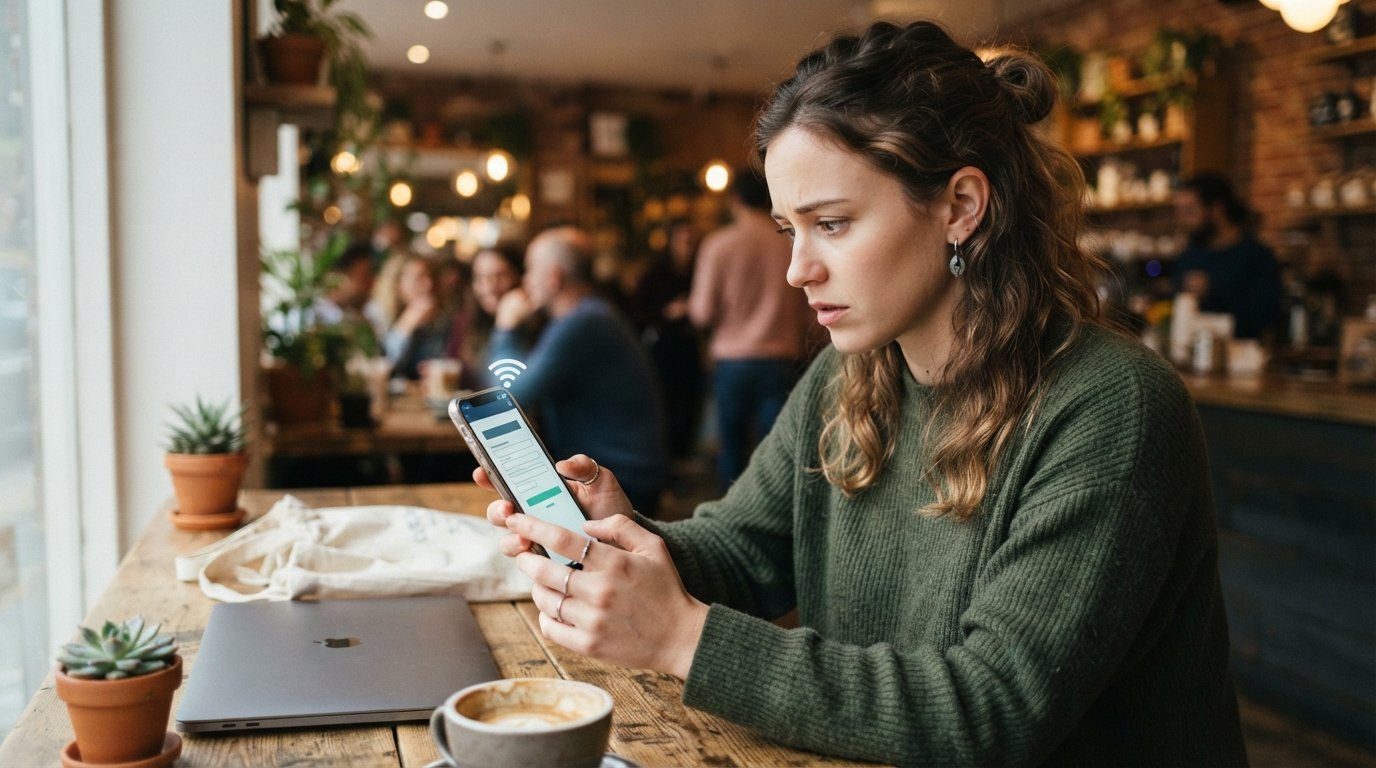
You are sitting in a coffee shop, staring at your phone, and you need to submit an online loan request form quickly. The Wi-Fi is free, the deadline is real, and your banking details are ready. But a nagging question slows your thumb: are online loan request forms safe on public Wi-Fi? The answer is not a simple yes or no. It depends on how the form is built, how the network is configured, and what you do before you hit submit. Understanding the layers of risk and protection can help you act fast without exposing your financial life to strangers.
The Short Answer: It Depends on Encryption and Behavior
When you submit a loan request form on a public network, your data travels from your device to the lender's server through radio waves and routers you do not control. If the form uses strong SSL encryption and you take basic precautions, the risk is low. If either of those conditions fails, your information can be intercepted or redirected. The good news is that reputable loan connection services, including LendersCashLoan, use 256-bit SSL encryption to protect data in transit. The bad news is that encryption only covers the tunnel between your browser and the website, not the network itself.
Public Wi-Fi networks are shared spaces. The person at the next table could be running software that monitors traffic, or the router itself could be compromised. That does not mean every public network is dangerous, but it does mean you should treat them differently from your home or office connection. The question is not whether public Wi-Fi is always unsafe, but whether the specific form and your specific habits reduce the risk to an acceptable level.
How SSL Encryption Protects Your Loan Request Data
SSL (Secure Sockets Layer) encryption, now more commonly called TLS, creates a private channel between your browser and the website. When you load a loan request form, the site presents a digital certificate, and your browser verifies it. If the certificate is valid, your browser and the server agree on encryption keys. From that point on, everything you type, including your name, address, income, and bank account details, is scrambled before it leaves your device.
For an eavesdropper on the same Wi-Fi network, encrypted data looks like random noise. Even if they capture the packets, they cannot read your Social Security number or bank routing information without breaking the encryption, which is impractical for most attackers. This is why you should never submit financial information on a page that does not show a padlock icon and an https prefix. The absence of those signals means your data is traveling in plain text, visible to anyone with basic network tools.
However, SSL has limits. It protects data in transit, not the server itself. If the lender's database is later breached, encryption during transmission will not help. It also does not protect you from a fake website that uses a valid certificate for a look-alike domain. And it does not stop malware on your own device from capturing what you type before it is encrypted. SSL is necessary but not sufficient, especially on a public network.
Why Public Networks Still Carry Risk Beyond the Website
Even when the loan request form is encrypted, the public network introduces risks that have nothing to do with the website itself. One common threat is the rogue access point, also known as an evil twin. An attacker sets up a Wi-Fi network with a name similar to the legitimate one, such as "CoffeeShop_Free" instead of "CoffeeShop_Guest." When you connect, all your traffic passes through the attacker's device. If you ignore certificate warnings or click through security prompts, you could be sending data to a server controlled by the attacker.
Another risk is DNS spoofing. The Domain Name System translates website names into IP addresses. On a compromised network, an attacker can redirect you from your intended lender's site to a fake page that looks identical. Your browser might show a valid certificate for the fake domain, which is why you should always check the address bar carefully. A misspelled domain or an unusual extension is a red flag.
Public networks can also expose your device to direct attacks. If file sharing is enabled or your firewall is weak, other users on the network may be able to access files or services on your device. This is less of a concern on a modern phone with default settings, but it is still worth disabling sharing features before connecting. The bottom line is that the network itself is part of your attack surface, and you cannot assume the operator has secured it.
Practical Steps to Submit a Loan Request Safely
If you must submit an online loan request form while away from a trusted network, you can reduce the risk with a few practical steps. The goal is to avoid relying on the public Wi-Fi for sensitive transmissions whenever possible, and to add layers of protection when you cannot avoid it.
- Use your mobile hotspot instead of public Wi-Fi. Your phone's cellular data connection is encrypted by the carrier and is far more private than a shared network. Tethering your laptop or using your phone directly for the form is the single most effective step you can take.
- Verify the website address and certificate. Before typing any personal information, check that the URL is exactly what you expect and that the padlock icon is present. Click the padlock to view the certificate details if you are unsure.
- Use a private or incognito browser window. This prevents your browser from storing form data and cookies on a shared device, and it reduces the risk of session hijacking if you step away.
- Turn off auto-connect and file sharing. Disable Wi-Fi auto-connect on your device and turn off any file or printer sharing features before joining a public network.
- Submit only on a secure form and log out immediately. After submitting, close the browser tab, clear your history if you are on a shared device, and log out of any account you created.
These steps do not make public Wi-Fi perfectly safe, but they significantly lower the odds that your loan request data falls into the wrong hands. The most important habit is to treat public networks as untrusted by default and to use cellular data for anything involving money or identity.
What Information to Have Ready Before Starting a Request
Preparation reduces the time you spend on a public network and lowers the chance of mistakes. Before you open a loan request form, gather the details you will need so you can complete the process in one focused session. Most short-term loan connection services ask for basic personal and financial information, and having it ready means you are not fumbling through your wallet or email while others are around.
- Your full legal name, date of birth, and government-issued ID number.
- Your residential address and contact information, including a valid email and phone number.
- Employment details and monthly income, which lenders use to assess eligibility.
- Your bank account number and routing number for potential funding and repayment.
- A list of any existing debts or obligations if you are seeking consolidation options.
Having these items ready also helps you avoid saving them in notes on a public device or emailing them to yourself, which creates additional copies of sensitive data. If you are using a loan connection service like LendersCashLoan, the request form is designed to be completed in under five minutes, so preparation is the key to speed and safety. For a broader look at how to evaluate lender legitimacy, see our guide on safe online loan lenders.
Recognizing a Secure Request Form Versus a Look-Alike Page
Not every page that asks for your bank details is legitimate, even if it looks professional. A secure loan request form should have several verifiable signals. The URL should match the company's official domain, the connection should be encrypted with a valid certificate, and the page should include clear privacy and consent disclosures. Reputable services explain how your data is used and provide contact information, including a phone number and physical address.
Look-alike pages often have subtle flaws. The domain might use a different top-level extension, such as .net instead of .com, or add a hyphen or extra word. The certificate may be valid for a different domain than the one you intended to visit. The page might pressure you to act immediately, omit privacy policies, or ask for information that is not relevant to a loan request, such as your social media passwords. Trust your instincts: if something feels off, close the page and navigate to the lender's site directly from a search engine or a known bookmark.
You can also check for third-party trust signals, such as SSL encryption statements and clear disclosures about the company's role. LendersCashLoan, for example, states that it is a loan connection service, not a direct lender, and that it uses 256-bit SSL encryption to protect your data. That kind of transparency is a good sign. If a site hides its identity or makes unrealistic promises like guaranteed approval with no credit check, treat it as a red flag.
How Loan Connection Services Add a Layer of Security
A loan connection service like LendersCashLoan does not lend money directly. Instead, it collects your request and shares it with a network of third-party lenders who may make you an offer. This model has security implications. On one hand, you are submitting your information to a single service rather than to multiple lenders, which reduces the number of times your data travels over the network. On the other hand, you are trusting that service to handle your data responsibly and to share it only with vetted partners.
Reputable connection services use encryption, limit access to your data, and provide clear disclosures about how your information is used. They also typically welcome applicants with less-than-perfect credit, which means they have processes in place to handle a wide range of financial situations. If you are exploring short-term options, you can use a service like ExpressCash to connect with lenders, but always verify the site's security signals before submitting anything. For LendersCashLoan users, the request process is designed to be simple and encrypted, but the same rules apply: use a trusted network when possible and verify the page before you type.
It is also worth remembering that short-term loans are not a long-term financial solution. They can help with an unexpected expense, but they should be used carefully and repaid on time. The security of your data is one part of responsible borrowing; the other part is understanding the terms, fees, and repayment schedule before you accept an offer.
Building a Safer Habit for Online Loan Requests
The safest approach is to avoid public Wi-Fi for any financial transaction, including loan request forms. Use your cellular data or a trusted home network whenever possible. If you must use public Wi-Fi, treat it as a last resort and take the steps outlined above: verify the site, use a hotspot if you can, avoid saving data, and log out immediately. These habits protect not only your loan request but also your banking, shopping, and email accounts.
Security is a practice, not a product. No single tool will make public Wi-Fi completely safe, but combining encryption, careful browsing, and good judgment reduces the risk to a manageable level. When you understand how SSL works, why public networks are risky, and how to spot a fake form, you can make informed decisions about when and where to submit sensitive information. That knowledge is your best defense, whether you are applying for a loan or simply checking your balance.